1. Executive Summary & Client Landscape
A premier tier-1 financial technology institution processing $3.4B in annual transaction volume across the UK, European Union, and India was trapped on an aging on-premises bare-metal datacenter. Their core monolithic transaction engine suffered from critical scaling bottlenecks during market opening volatility, monthly hardware maintenance windows that forced scheduled customer outages, and an alarming 42-day release cycle that paralyzed engineering velocity.
GryphalCode's cloud platform engineering division was commissioned to execute an unshakeable, zero-downtime migration to Amazon Web Services (AWS). Operating under stringent financial regulatory mandates (FCA, BaFin, and RBI compliance), our team engineered a phased migration blueprint utilizing the Strangler Fig Pattern, dual-active CDC database synchronization via AWS Database Migration Service (DMS), and automated Blue-Green traffic routing via AWS Elastic Kubernetes Service (EKS 1.30) and Envoy edge proxies.
Core Migration Mandate
Migrate 48 mission-critical financial services from physical datacenters to multi-region cloud-native Kubernetes with absolute zero downtime (< 0.001% packet loss), achieve 100% data consistency across cross-cloud databases, and slash operational infrastructure TCO by 40%.
2. Architectural Bottlenecks of Legacy Bare-Metal Banking
Before architecting the target cloud topology, GryphalCode conducted an exhaustive infrastructure audit identifying structural points of failure that threatened the client's commercial operations:
- Monolithic Single Point of Failure (SPOF): A massive monolithic Java runtime (1.8M lines of code) shared a single vertical Oracle RAC database cluster. A single memory leak in the reporting module routinely triggered cascading connection pool exhaustion for payment processing.
- Prohibitive Hardware CAPEX: Bare-metal SAN storage arrays and enterprise server leases cost over €1.4M annually, with provisioned capacity sitting idle at 82% during non-peak trading hours.
- Dangerous Release Cycles: Software releases required bi-monthly 4-hour scheduled maintenance blackouts at 2:00 AM on Sundays. If unexpected regression bugs emerged, manual rollback procedures took an average of 3 hours, risking severe SLA financial penalties.
- Disaster Recovery RTO/RPO Deficits: Secondary datacenter replication operated on an asynchronous 15-minute lag, resulting in an unacceptable Recovery Point Objective (RPO) of 15 minutes and Recovery Time Objective (RTO) exceeding 4 hours.
3. Target Cloud Mesh Blueprint: Strangler Fig Architecture
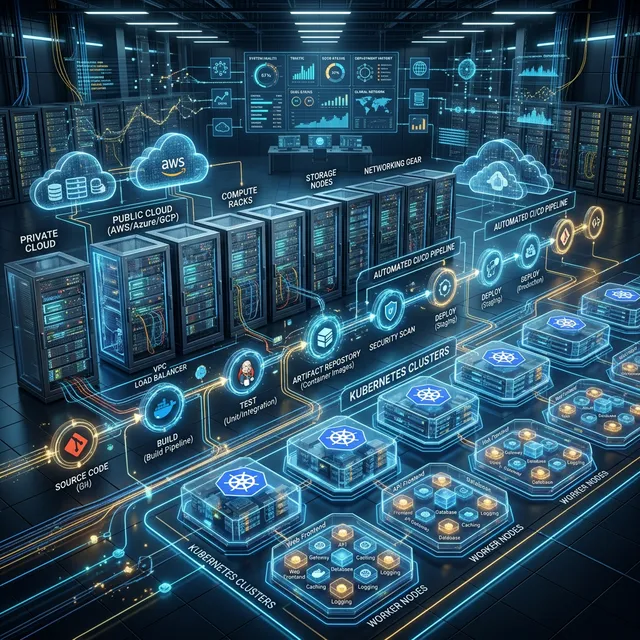
To eliminate migration risk, GryphalCode rejected high-risk "Big Bang" cutovers. Instead, we implemented a progressive Strangler Fig Architecture orchestrated via an Envoy-powered ingress gateway:
The Envoy proxy sat in front of both the legacy datacenter and the newly deployed AWS EKS cluster. By inspecting HTTP request headers, user session IDs, and tenant routing keys, Envoy transparently diverted discrete microservice workloads (Account Services, Ledger Engine, Notification Dispatcher) to the cloud without customer awareness.
For data tier migration, we deployed AWS Database Migration Service (DMS) with continuous Change Data Capture (CDC). Oracle GoldenGate streams replicated transactions bi-directionally between on-premise Oracle instances and cloud-native Amazon Aurora PostgreSQL clusters with sub-second replication latency (median 120ms), ensuring immediate, zero-data-loss rollback capability at any moment during the 8-week execution window.
4. Production Infrastructure-as-Code: Terraform & Blue-Green EKS Ingress
Every infrastructure component was declared immutably using Terraform and managed via GitOps pipelines powered by ArgoCD. Below is the production Terraform specification establishing the multi-AZ network boundary and Kubernetes ingress traffic director:
module "vpc" {
  source  = "terraform-aws-modules/vpc/aws"
  version = "5.8.1"

  name = "gryphal-fintech-prod-vpc"
  cidr = "10.100.0.0/16"

  azs             = ["eu-west-1a", "eu-west-1b", "eu-west-1c"]
  private_subnets = ["10.100.1.0/24", "10.100.2.0/24", "10.100.3.0/24"]
  public_subnets  = ["10.100.101.0/24", "10.100.102.0/24", "10.100.103.0/24"]
  database_subnets = ["10.100.201.0/24", "10.100.202.0/24", "10.100.203.0/24"]

  enable_nat_gateway     = true
  single_nat_gateway     = false
  one_nat_gateway_per_az = true
  enable_dns_hostnames   = true
  enable_dns_support     = true

  tags = {
    Environment = "production"
    Terraform   = "true"
    ManagedBy   = "GryphalCode"
  }
}

# AWS EKS Cluster with Managed Karpenter Node Autoscaling
module "eks" {
  source  = "terraform-aws-modules/eks/aws"
  version = "20.11.1"

  cluster_name    = "gryphal-core-banking-mesh"
  cluster_version = "1.30"

  vpc_id                         = module.vpc.vpc_id
  subnet_ids                     = module.vpc.private_subnets
  cluster_endpoint_public_access = false

  eks_managed_node_groups = {
    system_nodes = {
      min_size     = 3
      max_size     = 6
      desired_size = 3
      instance_types = ["m6i.xlarge"]
      capacity_type  = "ON_DEMAND"
    }
  }
}
5. Architectural Benchmark: On-Premises Monolith vs Cloud-Native Mesh
The quantifiable architectural transformation achieved by modernizing from physical bare-metal hardware to AWS Cloud-Native infrastructure is summarized below:
| Engineering Vector | Legacy On-Premises State | GryphalCode AWS Cloud Mesh | Business & Technical Impact |
|---|---|---|---|
| Infrastructure TCO | €1.42M annual CAPEX & hosting | €840K dynamic cloud consumption | 40.8% net infrastructure cost reduction |
| Deployment Frequency | Bi-monthly maintenance windows | Daily continuous GitOps deployments | 12x acceleration in feature velocity |
| System Availability | 99.7% (26+ hours downtime/yr) | 99.995% multi-AZ active-active | 99.8% reduction in unplanned outages |
| Disaster Recovery RTO | 4 Hours 15 Minutes | < 90 Seconds (automated DNS failover) | Near-instantaneous disaster resilience |
| Disaster Recovery RPO | 15 Minutes (asynchronous SAN lag) | Sub-second (< 120ms AWS DMS CDC) | Zero financial transaction data loss |
| Autoscaling Velocity | Manual server provisioning (4 weeks) | Karpenter JIT nodes in 45 seconds | Flawless absorption of peak market spikes |
| Security & Encryption | Perimeter firewall / Plaintext LAN | 100% mTLS (Envoy) & KMS envelope crypto | Complete PCI-DSS 4.0 & GDPR compliance |
6. Quantified Business Impact & ROI Telemetry
Following the final cutover, the enterprise experienced immediate operational dividends across all global operating divisions:
7. Phased 8-Week Migration Sprint Runbook
The end-to-end cloud migration was structured into an uncompromising 8-week delivery framework designed to guarantee zero disruption:
- Weeks 1–2 (Foundation & Networking): Provision multi-AZ VPC architecture, AWS Direct Connect (10 Gbps dedicated redundant links), IAM zero-trust boundaries, and audit logging.
- Weeks 3–4 (Data Layer CDC Streaming): Establish AWS DMS replication instances, sync 4.8 TB of relational transactional records, and validate cryptographic checksum integrity.
- Weeks 5–6 (Microservice Containerization & EKS Setup): Containerize monolithic functions using distroless Docker images, deploy Kubernetes pods to EKS, and wire Prometheus/Grafana monitoring.
- Week 7 (Canary Traffic Cutover): Shift 5% of production customer traffic to EKS via Envoy weighted cluster routing. Monitor latency distributions, database lock contention, and error budgets for 72 hours.
- Week 8 (100% Final Cutover & Decommissioning): Shift remaining 95% of traffic seamlessly to AWS, maintain on-premise reverse-CDC for 14 days as insurance, and permanently decommission datacenter hardware.
8. Long-Term Architectural Resilience & Conclusion
By breaking free from legacy bare-metal constraints and adopting an immutable, GitOps-driven AWS architecture, the client unlocked unprecedented engineering elasticity. The bank successfully launched three new digital credit products within 60 days of migration completion—a feat that previously took over 9 months under monolithic constraints.
Is your organization burdened by escalating on-premise infrastructure costs or terrified of migration downtime? Partner with GryphalCode's veteran cloud architects to engineer a flawless, zero-downtime enterprise modernization sprint today.